Blog
Attackers Extract Microsoft Edge Passwords From Memory Using Legitimate Remote Access Tools
- May 06, 2026
-

An attacker who has administrative-level access can retrieve Microsoft Edge users’ saved passwords from memory, even when those credentials are not actively being used. This is possible because the browser temporarily keeps them in an unencrypted form in its process memory as part of how it is designed. According to a new report from Securonix,…
Why Windows Co-Management Is Becoming a Smarter Path for Enterprise IT
- May 06, 2026
-

It isn’t hard to guess why Microsoft Intune is a common first choice for Windows device management. For enterprises already using Microsoft 365 and Entra ID, it offered a logical way to extend modern management to Windows devices while keeping administration aligned with the broader Microsoft ecosystem. But as device estates grow and operational demands…
Millions of Internet‑Exposed RDP and VNC Servers Threaten Critical Systems
- May 05, 2026
-
RDP vulnerabilities have become a critical but often overlooked risk for organizations worldwide, which leaves many systems unknowingly exposed. Cyber attackers are increasingly exploiting these gaps by using unsecured servers as easy entry points into enterprise networks. According to a new report from Forescout Vedere Labs, millions of RDP and VNC servers are publicly accessible…

Active Directory DNS: Why It’s Required and How It Actually Works
- May 05, 2026
-

Active Directory DNS is used to locate domain controllers and critical services (LDAP, Kerberos, and the Global Catalog) via SRV and host records. If DNS is missing or misconfigured, common outcomes include failed logons, Group Policy errors, and domain controller replication issues. This article explains how and why Active Directory depends on DNS, with practical…
Why Over‑Privileged Apps Are One of the Most Dangerous Attack Paths in Microsoft Entra
- May 05, 2026
-
Russell Smith
 Russell Smith
“Applications can be incredibly powerful. If you own the application, you can act as that application. And if that application is highly privileged, you could effectively become a global admin without ever being in that group.” Nicolas Blank, Identity Architect, Microsoft MVP, and CTO of NBConsult In Microsoft Entra, being an application owner can be…
Microsoft Previews User‑Initiated Provisioning for Windows 365 Reserve
- May 04, 2026
-
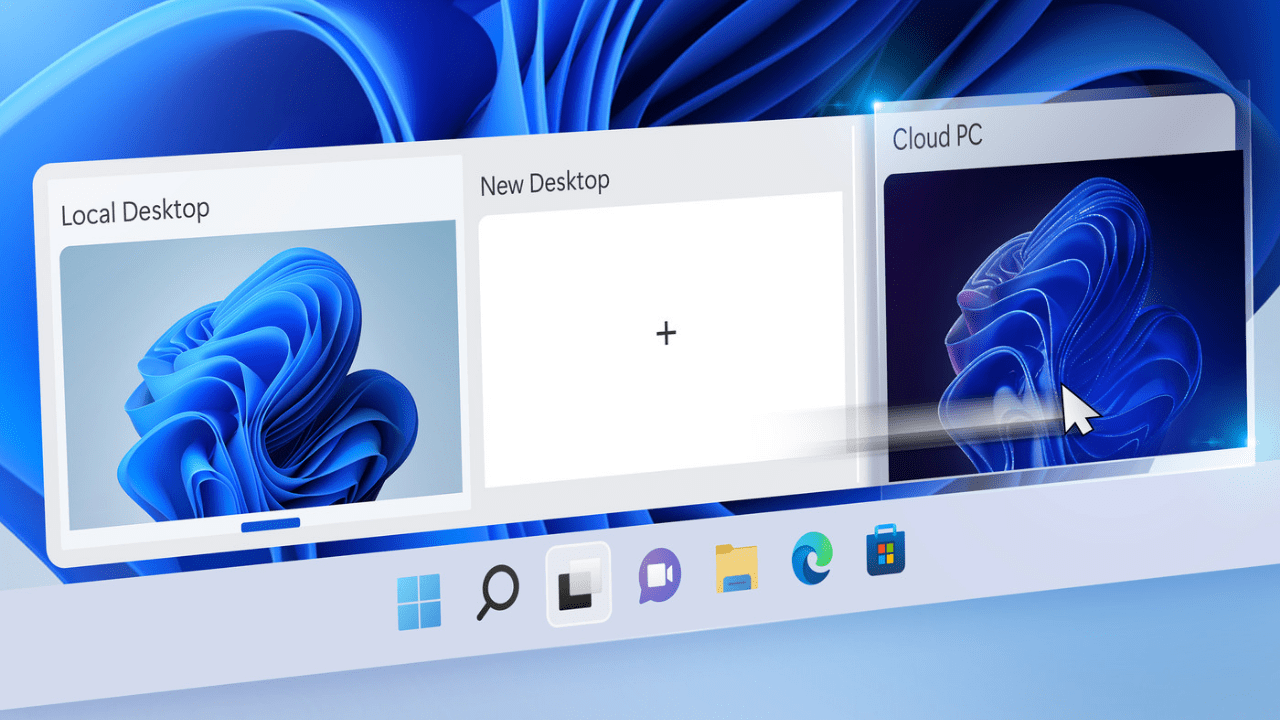
Microsoft has introduced a public preview of user-initiated provisioning for Windows 365 Reserve. The feature enables selected users to spin up their own Reserve Cloud PC on demand, reducing reliance on IT administrators and minimizing downtime. Windows 365 Reserve is a cloud‑based service that provides employees with a temporary, fully configured virtual Windows PC when…
Microsoft Intune Adds Real‑Time App Inventory, Linux SSO Enhancements
- May 04, 2026
-
Microsoft is rolling out a series of enhancements to Microsoft Intune, targeting deeper visibility and tighter control across modern endpoints. This month’s updates span improved Windows app inventory, a more secure Linux SSO experience, and expanded enrollment and management capabilities for Apple devices. Microsoft has added new enhanced app inventory capabilities in the “All Apps”…
First Ring Daily: Microsoft Earnings Aftermath
- May 01, 2026
-
In this episode of First Ring Daily, Brad Sams and Paul Thurrott discuss Microsoft’s blockbuster earnings results for the first quarter of 2026.
Microsoft Agent 365 Adds New Tools to Discover and Govern AI Agents
- May 01, 2026
-
Microsoft has announced the general availability of Agent 365, which first entered preview in November 2025. Alongside the release, the company introduced new capabilities designed to help organizations discover, monitor, and manage both sanctioned agents and shadow AI across their environments. Microsoft Agent 365 is designed to give organizations a centralized way to monitor, manage,…

Microsoft Sets Unified RBAC as Default for New Defender Tenants
- Apr 30, 2026
-
Microsoft is set to make unified role-based access control (RBAC) the default permission model for all new Microsoft Defender for Office 365 environments. The company is also rolling out more granular email access controls to give security teams tighter, more precise control over sensitive data. Starting on May 30, Unified RBAC will be enabled by…
Windows Zero‑Day Vulnerability Enables NTLM Credential Theft
- Apr 30, 2026
-
Microsoft and the CISA have issued an urgent alert to federal agencies over a newly discovered Windows zero-day vulnerability. The flaw could enable attackers to silently extract sensitive data from affected systems. According to a new report from cybersecurity firm Akamai, CVE‑2026‑32202 is a Windows vulnerability that emerged due to an incomplete fix for an…
Microsoft to Block Legacy TLS Connections for POP and IMAP in Exchange Online
- Apr 29, 2026
-
Microsoft is strengthening security in Exchange Online by retiring support for outdated email encryption methods. Beginning in July 2026, organizations still using legacy TLS versions for POP3 and IMAP4 connections may experience service disruptions unless they transition to modern encryption standards. The change is part of Microsoft’s broader effort to eliminate aging security protocols that…