
Rabia Noureen
News EditorRabia has a master's degree in Software Engineering and she has years of experience writing professionally about Microsoft products and other technologies. Rabia has also written for OnMSFT.com as well as Windows Report. She is always up to date on the latest trends in the IT Industry and has done extensive research in the data science industry.
LATEST
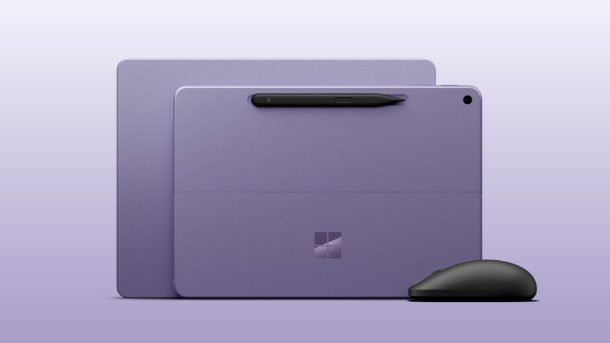
Microsoft Bets on Local AI Processing with New Surface Devices
- Sep 23, 2026
-
Microsoft has launched new 12-inch Surface Pro and 13-inch Surface Laptop devices powered by Qualcomm’s Snapdragon X2 Plus processor. The company is also launching a redesigned Surface Mouse that adds haptic feedback and deeper Copilot integration. These new Surface devices come as Microsoft continues to push AI-powered Copilot+ PCs. The company has highlighted significant gains…
AI-Powered Attacks are Exposing the Limits of Fragmented Security Operations
- Sep 23, 2026
-
Security operations teams are facing growing pressure as attackers use AI to automate cyberattacks at greater speed and scale. While threat actors are increasingly benefiting from automation, many organizations still rely on disconnected security tools that force analysts to move between separate platforms for detection, investigation, and response. This fragmentation can slow security teams at…
Organizations Still Relying on SMS MFA Face a Forced Move to Passkeys
- Sep 22, 2026
-
Microsoft is preparing a major shift in its authentication strategy by retiring its native SMS and voice-based multifactor authentication (MFA) services in Microsoft Entra ID. The company argues that traditional phone-based verification methods are increasingly vulnerable to phishing, SIM-swapping, and other social engineering attacks, which makes phishing-resistant authentication methods a better fit for modern security…
Organizations Face a Growing Gap Between Cyber Risks and Security Resources
- Sep 22, 2026
-
A new ISACA study found that cybersecurity teams are struggling to keep up with a growing volume of attacks while facing limited resources. More than a third of European IT and security professionals reported an increase in cyberattacks over the past year, yet many organizations continue to operate with insufficient staffing and funding. According to…
Windows Admin Center Combines Installation Paths, But a Key Limitation Remains
- Sep 21, 2026
-
Microsoft has been developing two separate experiences within Windows Admin Center, including Administration Mode (aMode) for general server management and Virtualization Mode (vMode) for managing Hyper-V and virtualization infrastructure. Having separate installation experiences created additional complexity for IT teams evaluating or deploying the platform, particularly those interested in trying the newer virtualization-focused capabilities. This separate…
Critical Cisco ISE Flaw Could Give Attackers Access Without Valid Credentials
- Sep 21, 2026
-
Organizations using Cisco Identity Services Engine (ISE) face an urgent security risk after a critical vulnerability was disclosed that could let attackers access management functions without valid credentials. The flaw, tracked as CVE-2026-76460, stems from insufficient authentication checks on a vulnerable API endpoint. According to Cisco, a remote attacker could send specially crafted requests to…

Windows 11 Security Update Triggers Active Directory Authentication Problems
- Sep 18, 2026
-
A recent Windows security update is creating unexpected authentication problems for some organizations that use on-premises Active Directory. After installing the September 2026 security update KB5124008, certain domain-joined Windows 11 devices can lose their secure trust relationship with the domain, which prevents users from signing in with valid domain credentials. This issue affects Windows 11…
AI Agent Sprawl is Creating New Governance Challenges for IT Teams
- Sep 17, 2026
-
As organizations deploy more AI agents across different platforms, IT teams often lack a centralized way to track, secure, and manage them. Agents built in different environments can operate with varying permissions, data access levels, and compliance controls, making oversight more complex. Microsoft warns that this fragmented approach can increase the risk of security gaps,…

Attackers are Turning Passkeys into a New Social Engineering Target
- Sep 17, 2026
-
Organizations are increasingly deploying passkeys and phishing-resistant authentication to strengthen identity security. However, Microsoft Security Research has found that attackers are exploiting employees’ familiarity with these technologies by using passkey-themed social engineering campaigns to gain access to cloud accounts and sensitive corporate data. According to Microsoft, the attacks typically begin with phone calls, text messages,…
Windows Server 2022 Customers are Running Out of Time to Plan Their Next Upgrade
- Sep 16, 2026
-
Organizations running Windows Server 2022 are approaching a critical milestone as the platform reaches the end of mainstream support on October 13, 2026. The operating system will continue receiving security updates under extended support until October 2031, but Microsoft will no longer provide the full range of mainstream support capabilities that many IT teams rely…
Businesses are Learning That Cyber Risk is an Ongoing Operational Expense
- Sep 16, 2026
-
Cyberattacks are becoming a routine cost of doing business rather than an occasional crisis. According to the Hiscox Cyber Readiness Report 2026, nearly one-third of organizations experienced a cyberattack in the past year. Organizations that suffer cyber incidents lose an average of 32 hours of operational productivity per attack and face annual cyber-related costs of…
Ransomware Operators are Exploiting a Critical VMware vCenter Flaw
- Sep 15, 2026
-
Organizations running VMware vCenter face growing risk from a critical remote code execution vulnerability (CVE-2026-59310) that ransomware operators are now actively exploiting. This flaw, which was patched by Broadcom in July, allows unauthenticated attackers to execute code on vulnerable systems, which makes exposed vCenter deployments a high-value target. VMware vCenter is a centralized management platform…