Rabia Noureen
News EditorRabia has a master's degree in Software Engineering and she has years of experience writing professionally about Microsoft products and other technologies. Rabia has also written for OnMSFT.com as well as Windows Report. She is always up to date on the latest trends in the IT Industry and has done extensive research in the data science industry.
LATEST
Microsoft 365 Direct Send Feature is Letting Hackers Steal Credentials — Are You at Risk?
- Jun 30, 2025
-

Security researchers have discovered a sophisticated phishing campaign that exploits Microsoft 365’s Direct Send feature, allowing attackers to send deceptive emails without authentication to steal user credentials. Since May 2025, this technique has targeted over 70 organizations across multiple industries in the U.S., posing a significant threat to enterprise email security. In Exchange Online, the…
Critical Vulnerabilities Expose Hundreds of Brother Printers to Remote Attacks
- Jun 27, 2025
-
Cybersecurity researchers have discovered critical vulnerabilities that affected hundreds of home and enterprise printers from the hardware manufacturer Brother. Security firm Rapid7 found that eight security flaws are affecting multifunction printers. Specifically, Rapid7 researchers have found eight serious vulnerabilities that affected 689 models of Brother devices, including printers, scanners, and label makers. These flaws also…
Microsoft Boosts Windows 11 Resilience with New Recovery and Security Tools
- Jun 26, 2025
-
Microsoft announced this morning the latest advancements in its Windows Resiliency Initiative (WRI). The company has detailed new tools to support resiliency on the Windows platform, including quick machine recovery, Microsoft Connected Cache, and more. Last year, Microsoft announced the Windows Resiliency Initiative (WRI) as a strategic effort to embed resilience and security directly into…
Microsoft Enables Hotpatching by Default for New Windows Quality Update Policies
- Jun 25, 2025
-
Microsoft has announced that the hotpatching feature is now enabled by default for all new Windows quality update policies created through Microsoft Intune. This new feature should help organizations improve security compliance and reduce downtime for Windows devices. Hotpatching is a Windows update feature that allows certain updates (especially security patches) to be applied without…
Microsoft Defender for Identity Gets Domain-Based Scoping to Streamline SOC Monitoring
- Jun 25, 2025
-
Microsoft Defender for Identity now supports domain-based scoping for Active Directory (AD) in public preview. This new feature allows SOC analysts to selectively define which AD domains fall within their monitoring scope to enhance focus and reduce noise. As organizations expand, their identity environments become increasingly complex, making it harder for security teams to manage…
Organizations Can Now Sign Up for Windows 10 Extended Security Updates
- Jun 24, 2025
-
Microsoft has announced updates to its Windows 10 Extended Security Updates (ESU) program. Starting today, organizations can enroll through the Microsoft Volume Licensing Program, with enrollment via Cloud Service Providers opening on September 1. Microsoft plans to end support for Windows 10 on October 14, 2025. After this date, the company will no longer provide…
Microsoft Defender for Office 365 ICES Vendor Ecosystem Boosts Email Security
- Jun 23, 2025
-
Microsoft has launched a new vendor ecosystem for Defender for Office 365, designed to seamlessly integrate trusted third-party email security solutions. This unified framework enhances threat protection, streamlines operations, and empowers organizations with greater visibility and control. The Microsoft Defender for Office 365 ICES vendor ecosystem addresses the growing complexity of email security by creating…
Misconfigured Cloud Storage Fuels False Sense of Security
- Jun 23, 2025
-
Tenable’s 2025 Cloud Security Risk Report reveals that 9% of publicly accessible cloud storage contains sensitive data, with 97% of it classified as restricted or confidential. This highlights an urgent need for IT leaders to address cloud misconfigurations, exposed secrets, and identity gaps before they escalate into security breaches. The Tenable Cloud Security Risk Report…
Microsoft to Phase Out Legacy Drivers from Windows Update to Strengthen Security
Last Update: Jun 23, 2025
- Jun 20, 2025
-
Microsoft is set to remove legacy drivers from Windows Update as part of a major push to strengthen system security and improve compatibility. This strategic move kicks off a broader initiative aimed at delivering only the most reliable and up-to-date drivers to Windows users. How does the driver cleanup process work? Microsoft says that the…
Microsoft 365 to Block Legacy Authentication by Default — Here’s What You Need to Know
- Jun 20, 2025
-
Microsoft is set to block legacy authentication protocols by default, which will cut off access to SharePoint, OneDrive, and Office files to enhance security. IT administrators are advised to prepare, as these default setting changes will roll out across Microsoft 365 tenants starting mid-July 2025. Why is Microsoft 365 blocking legacy authentication? Microsoft says this…
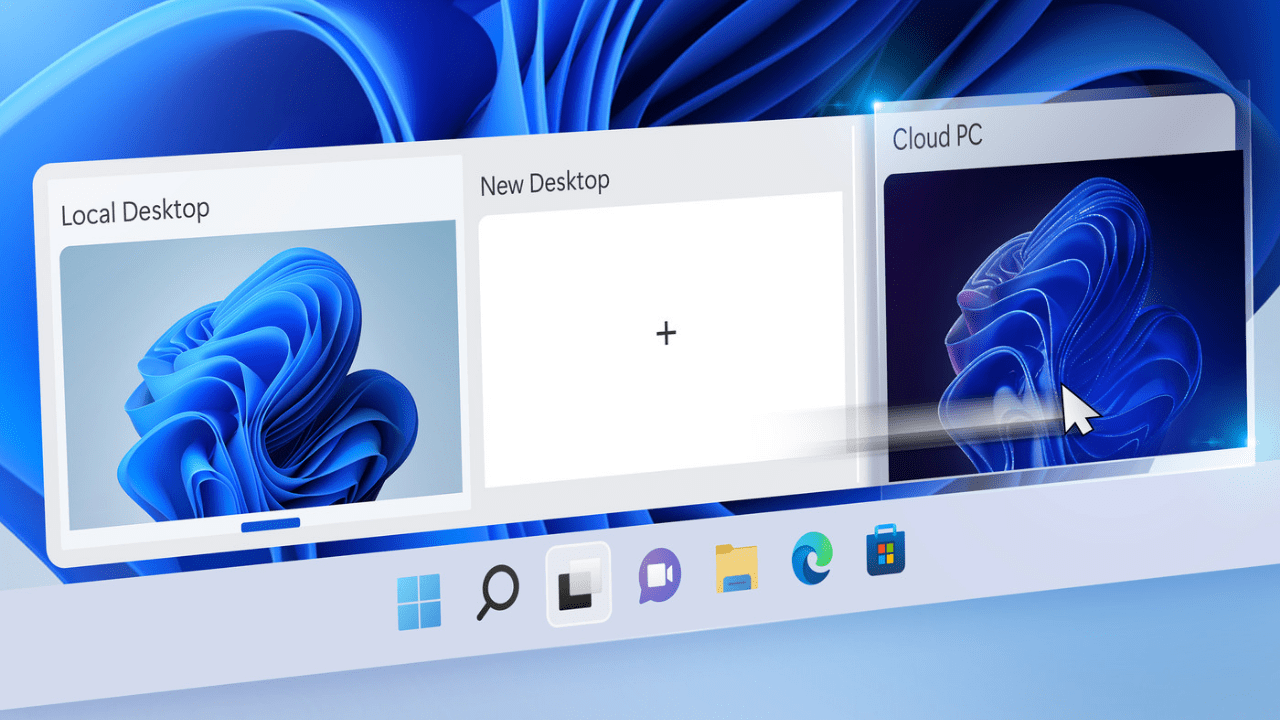
When Devices Fail, Windows 365 Reserve Cloud PCs Provide Continuity
- Jun 19, 2025
-
Microsoft has announced Windows 365 Reserve, now in public preview for commercial customers. This new offering gives employees immediate access to a temporary Cloud PC when their primary device is lost, stolen, delayed, or down. A recent survey of 1,000 IT decision-makers revealed that over three-quarters experienced device theft in the past two years. These…
Hackers Exploit Pentesting Tool in Massive Microsoft Entra ID Attack
- Jun 18, 2025
-
Cybersecurity researchers have discovered a widespread account takeover (ATO) campaign that weaponizes the TeamFiltration penetration testing framework to infiltrate Microsoft Entra ID (formerly Azure Active Directory) accounts. The attackers have already targeted over 80,000 user accounts across hundreds of organizations worldwide. TeamFiltration is a cross-platform penetration testing tool designed to simulate post-exploitation activities in Office…